


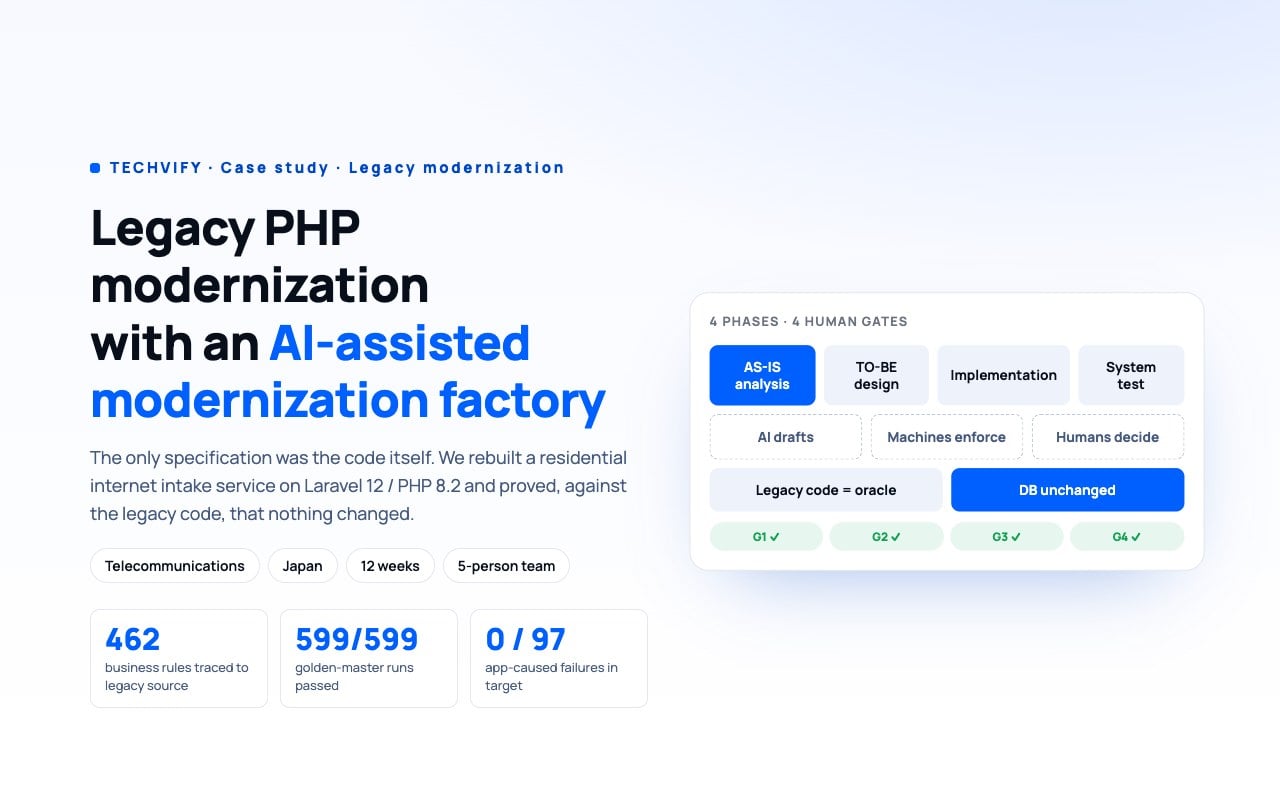
Legacy PHP platform rebuilt on Laravel 12 / PHP 8.2 for a Japanese telecommunications group, same database, same behaviour
12 wks
end-to-end delivery
462
rules traced to legacy source
599/599
golden-master runs passed
Eight incidents in ten days: leaked keys, a backdoored package, cracked certificate keys, runtime RCEs. None of them needed to hack you directly: Railway, LiteLLM, OpenCode, eMudhra, PHP and Node.js, GitLab, Plex, SBI.
Facts from the vendor advisories and Microsoft Threat Intelligence, and how fast Techvify can tell you where you stand.
Nobody has to hack you directly. One dependency, one provider or one over-privileged key is enough.
Infrastructure, packages, certificates, runtimes, source control, a bank. Different vendors, one lesson.
Customer environment variables accessed. Every user told to replace all secrets.
Release on PyPI and Docker Hub shipped a credential stealer and a backdoor.
OpenAI, Anthropic and Google keys stored by 1.4% of Console users may have been exposed.
Eight CA signing keys weak enough to crack; one private key was the number 4. Browsers revoked trust.
Emergency patches for remote code execution: PHP2Shell (two CVEs, CVSS 9.2) and Node2Shell (CVE-2026-111497, CVSS 9.2 on the CVE record). Express 5 and fetch() decompress Brotli automatically; Node 20 gets no fix.
Two unauthenticated RCE flaws rated CVSS 10.0, every self-managed release since 7.0.
Plex2Shell chain added to CISA’s exploited list; cryptominers seen installed in the wild.
3,897 customer records found on the dark web; source still unknown.
1 / 8
Microsoft Threat Intelligence attributes the ConnectWise supply-chain compromise to a China state-aligned actor using the ARTEX framework. Stolen application credentials let it operate without an interactive sign-in. In several cases, first contact to privileged cloud access took under three hours.
Apply the vendor fixes, restart every process, rebuild container images. National cyber-security agencies issued the same warning within a day.
Official advisories, linked to the source. Thumbnails show the first page of the public document.
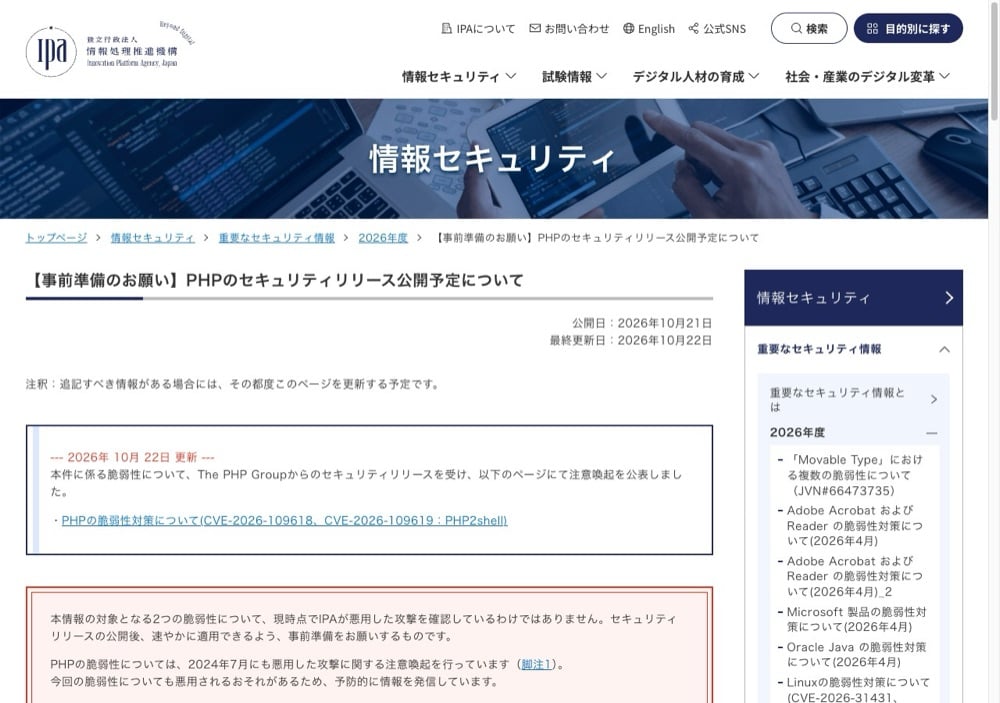
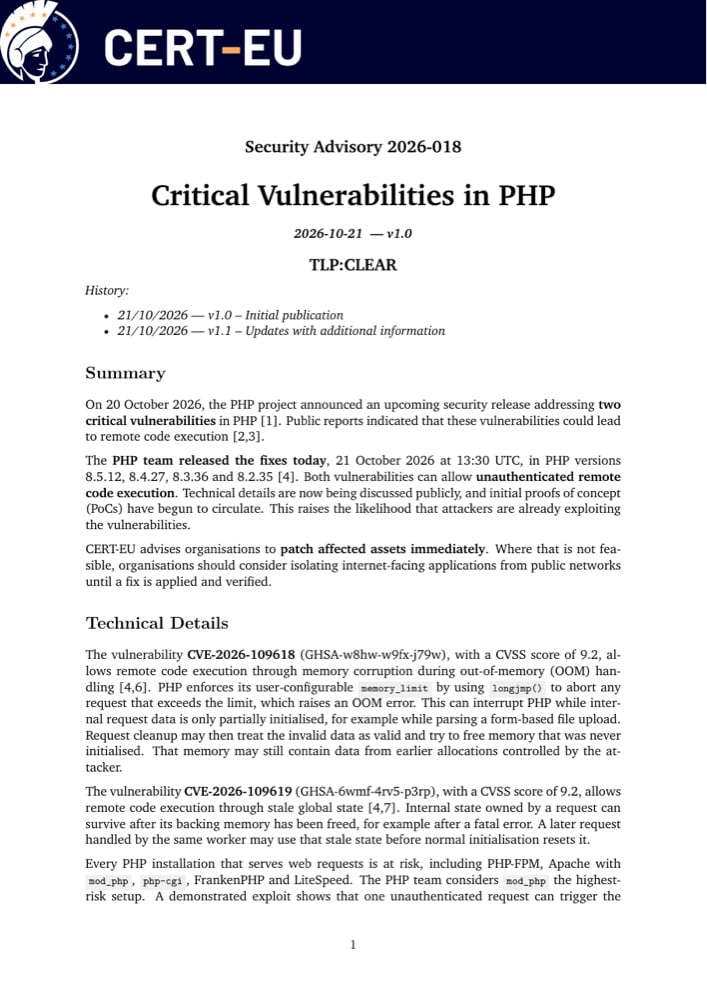
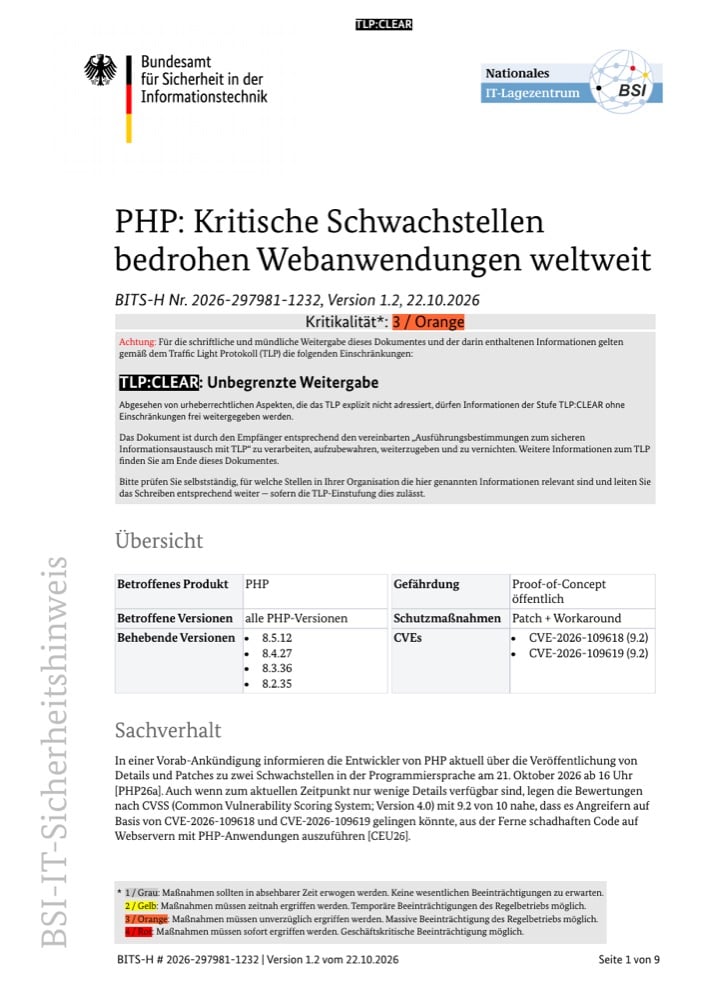
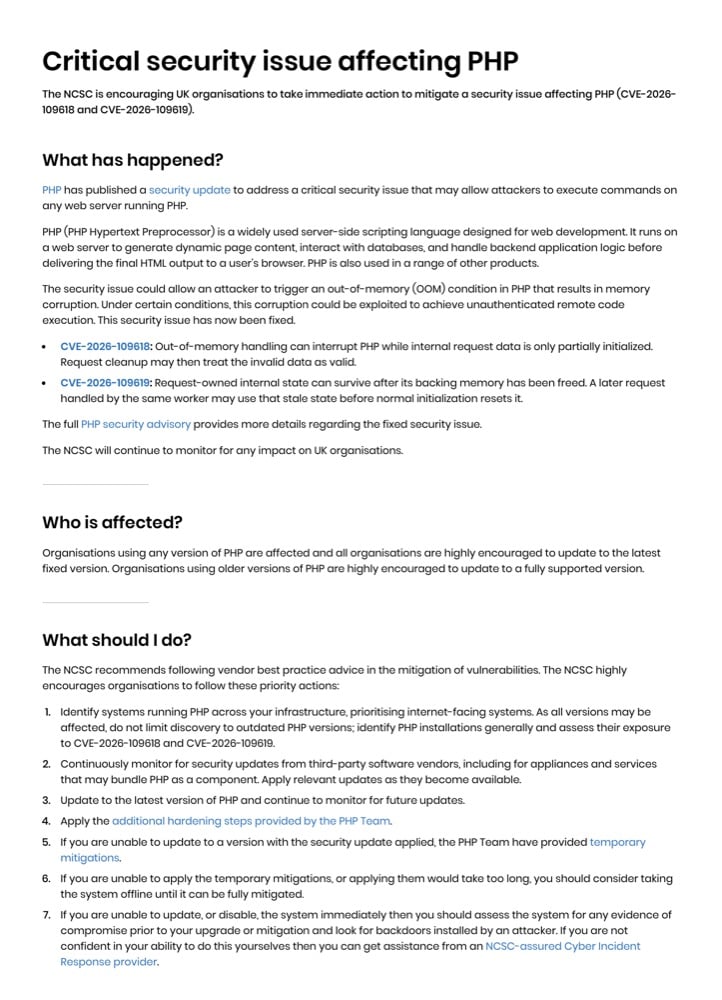
1 / 4
Source pages: IPA · CERT-EU · BSI · NCSC. Agency names belong to their owners; no endorsement of Techvify is implied.

Head Office
HUDTOWER Building, 37 Le Van Luong Str, Hanoi, Vietnam.
One compromised dependency, one infrastructure provider or one API key with too much access is enough to take the whole chain with it. Legacy systems cannot just bump a version. And the more access you hand to AI agents, the more one leaked credential can do.
One path, five steps, clear evidence at each.
Inventory services, dependencies, secrets and every agent with access.
A complete attack-surface inventory
Run dependency, secrets and exploitability checks against the inventory.
Risks ranked by real exposure
Recover what the legacy system really does before changing it.
A behavior baseline the rebuild must preserve
Patch, rotate and re-test until the original exploit path is closed.
Evidence-backed closure
Rebuild what cannot be patched on a pipeline that scans every build.
A guarded path to production
1 / 5
Delivered by a Techvify team. Together they form one release gate: one failure stops the release.
Dependency scan, secrets and key audit, and a review of what your AI agents can reach, in a day. Then an agent-run penetration test proves what is exploitable, with recorded evidence.
For systems that cannot just update. Recover what the system does from the source, then rebuild and test against that behaviour. Four review gates keep a named human accountable at every stage.
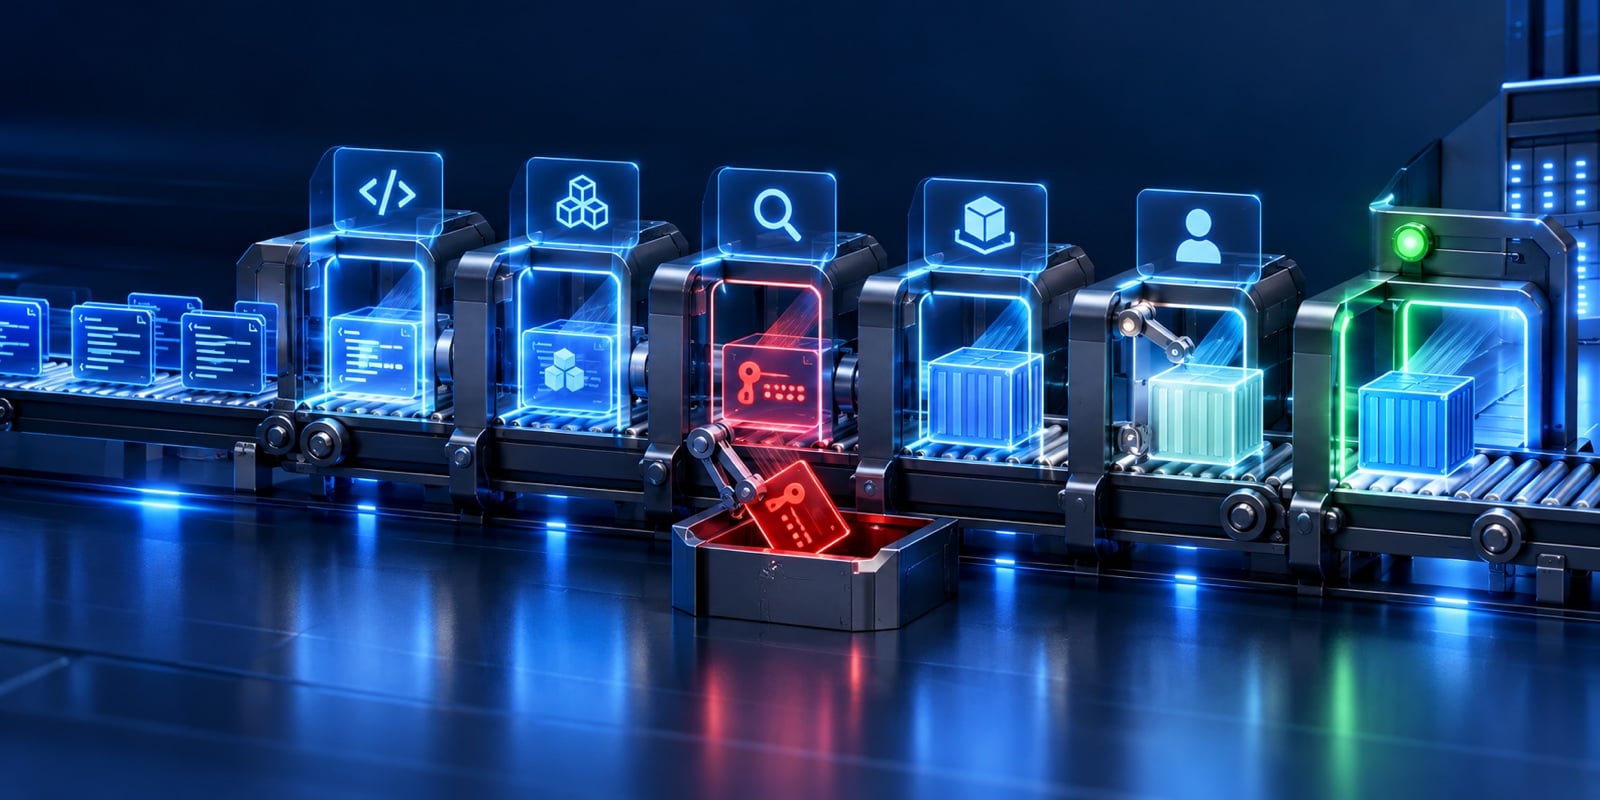
Security gates on every merge request stop vulnerable code, dependencies and leaked secrets before they reach a protected branch. Every build ships an SBOM, so the next critical CVE is a lookup, not a hunt.
1 / 3
The audit covers the whole path from dependency to deployment, not one runtime.
Book an audit
Independent standards and industry recognition behind the way we design, deliver and secure software.
1 / 4
Trusted by engineering and security teams at


Yes. Six of the eight incidents were not runtime bugs: leaked secrets, a backdoored package, cracked certificates, a data leak. The audit covers the chain, not one language.